Hi Imperva Community,
Greetings.
I recently executed the CIS Security Configuration Benchmark for PostgreSQL 16: Default Scan using Imperva DAM. However, the assessment reported several controls as Failed, even though the corresponding security configurations appear to be correctly implemented.
For example, the control related to the latest security patches being applied is reported as failed. However:
- The PostgreSQL instance is running the latest applicable version.
- The benchmark report itself correctly identifies the installed PostgreSQL version.
- The required security patches have already been applied.
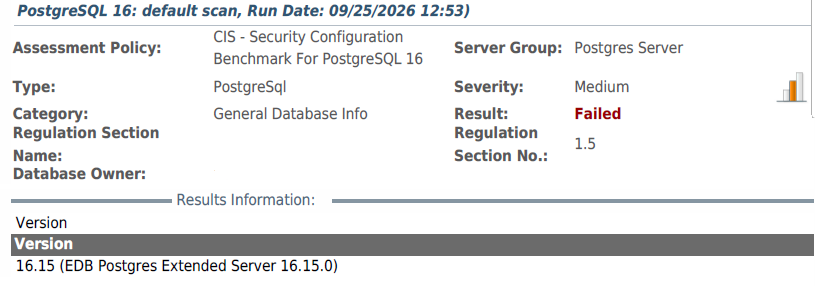
I have observed similar inconsistencies with a few other controls as well.
Could someone please clarify the following?
- Has anyone else encountered similar false failures while running the CIS benchmark scan for any database?
- How does Imperva DAM determine whether the installed database version has the latest security patches?
- Is there a supported method to review or customize the validation logic used by an individual benchmark test?
- Can a failed control be corrected or marked as compliant after providing appropriate technical evidence?
- Could this behavior indicate that the benchmark definitions or vulnerability intelligence require an update?
Any guidance on troubleshooting this issue or validating the test logic would be greatly appreciated.
Thank you.
#AllImperva#DatabaseActivityMonitoring------------------------------
Bharath Patil
Senior Manager
Karnataka Bank Ltd.
Bengaluru
------------------------------